

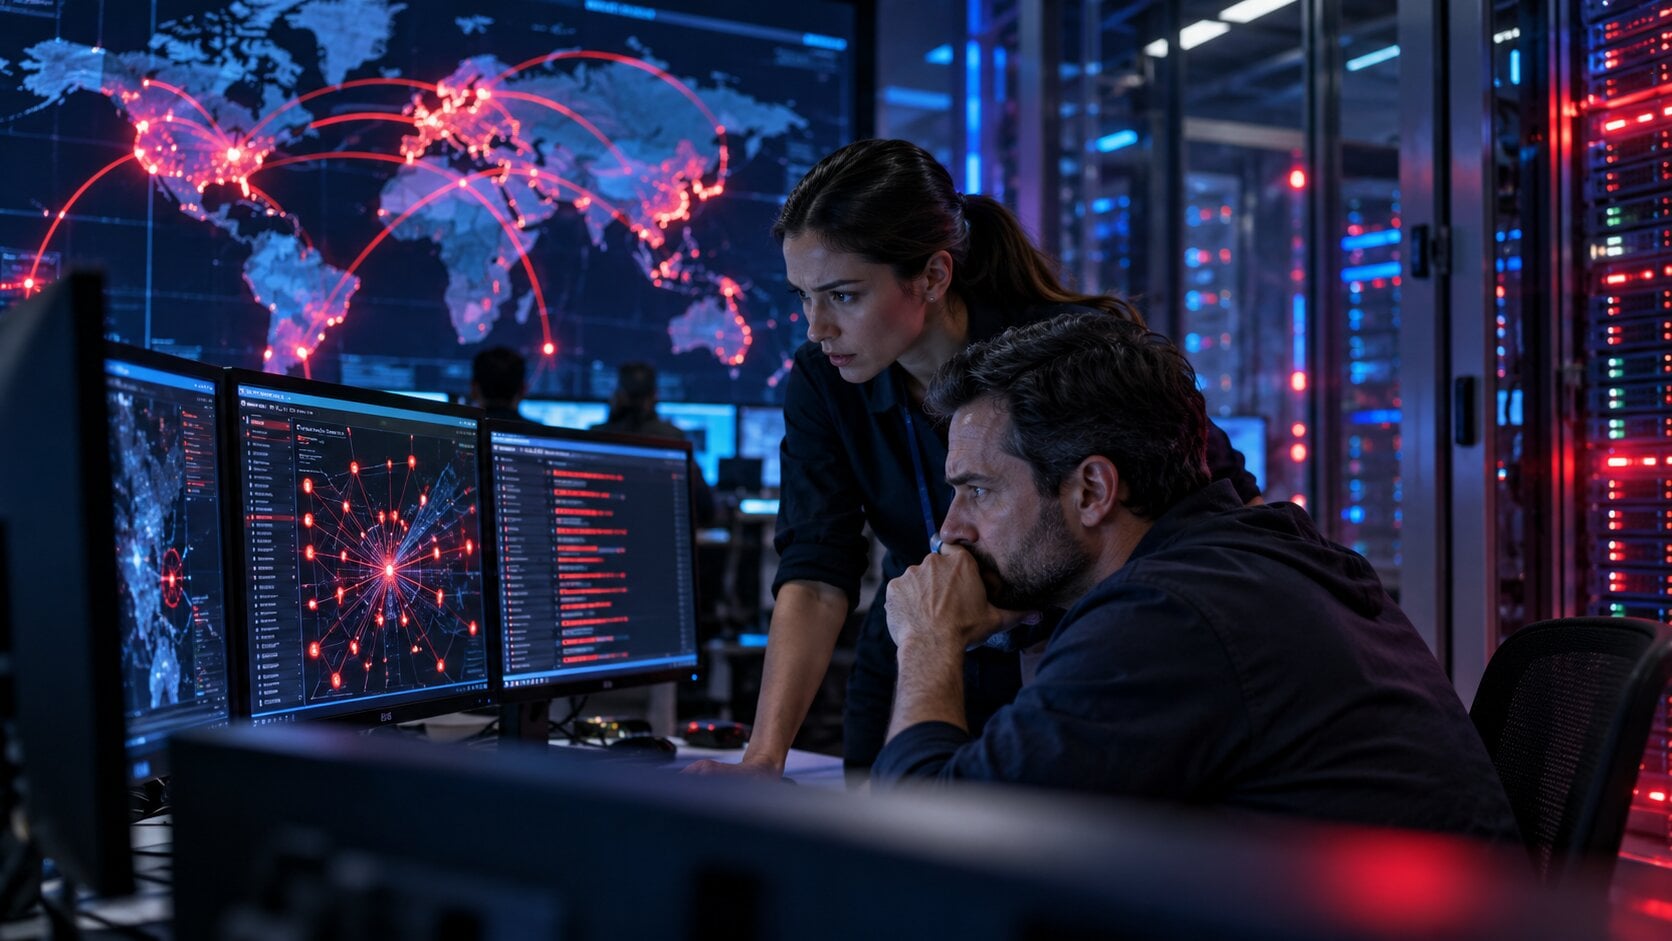
Two critical security vulnerabilities in the PHP programming language have triggered a global wave of cyberattacks. According to Cloudflare, the number of attempts to exploit these flaws reached millions within hours. Banks, airlines, and government institutions are temporarily shutting down online services as developers rush to deploy emergency security patches.
Hackers Launch Millions of Attacks Within Hours
The crisis was triggered by two critical vulnerabilities identified as CVE-2026-109618 and CVE-2026-109619. Both received a severity score of 9.2 out of 10 and could potentially allow attackers to execute malicious code remotely on affected servers without authentication.
According to Reuters, the vulnerabilities had remained undetected for years before being discovered with the assistance of artificial intelligence. Their public disclosure immediately sparked a race between cybersecurity teams and hackers.
Data from Cloudflare illustrates the scale of the threat. CEO Matthew Prince reported that the company’s network had detected thousands of exploitation attempts even before the official announcement.
Within 45 minutes of disclosure, that number surged to tens of thousands. Within two hours, it reached hundreds of thousands before eventually climbing into the millions.
However, these figures do not necessarily indicate successful breaches. Instead, they demonstrate how quickly cybercriminals can respond when previously unknown security weaknesses become public.
Banks and Governments Shut Down Online Services
The impact has been particularly significant in Japan. Financial institutions Mitsubishi UFJ and Nomura, airline ANA, and railway operator East Japan Railway temporarily suspended certain online services as a precaution.
Japanese government agencies also implemented emergency restrictions. Meanwhile, Finland temporarily shut down several government websites, and French telecommunications giant Orange restricted access to some applications.
China’s Ministry of Industry urged organizations to immediately inspect their systems, while South Korea raised its cybersecurity alert level.
PHP developers have released patched versions 8.2.35, 8.3.36, 8.4.27, and 8.5.12. The European Union Agency for Cybersecurity (ENISA) has recommended installing security updates immediately, particularly on publicly accessible servers.
The incident could also affect websites built on WordPress, which relies heavily on PHP. Updating WordPress alone may not be sufficient because the vulnerabilities exist within the underlying programming language itself.
In my view, this crisis also highlights the darker side of artificial intelligence. While AI helps security researchers identify dangerous vulnerabilities, it can also enable attackers to exploit them much faster.
As a result, the speed at which organizations detect threats and deploy security updates is becoming increasingly important.
